Wake the on-call analyst
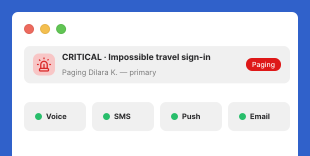
When a critical attack is confirmed, ITOC360 pages the on-call responder by voice, SMS, push, or email, not one more unread channel message.
Security Operations
ITOC360 takes the critical alerts your SOC and SIEM already produce and puts a named analyst on them in seconds, with escalation that runs until someone responds and an audit trail that holds up under review.
Your SIEM and SOC automations are good at detection. The gap is ownership: a confirmed intrusion that no one has picked up is not a response, it is dwell time, and every minute of it is room for an attacker to move laterally. ITOC360 closes that gap and puts a named responder on the alert before that window opens.
When a critical attack is confirmed, ITOC360 pages the on-call responder by voice, SMS, push, or email, not one more unread channel message.
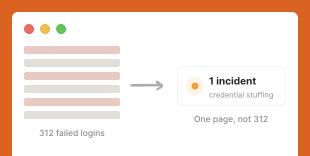
AI grouping and deduplication collapse repeat signatures and failed-login floods into a single incident, so analysts act on real intrusions instead of noise.
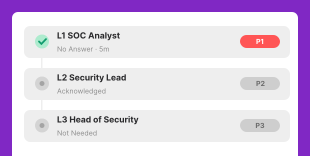
Multi-level chains with team and time-based rules send P1 attacks to the right specialist and hand off automatically if no one acknowledges.
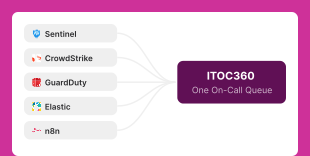
Native integrations with leading SIEM, XDR, and cloud security tools, plus n8n and Zapier. Keep your detection and SOAR logic unchanged.
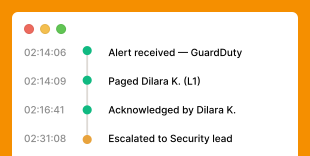
Every alert, acknowledgment, and escalation hop is logged with a secure timestamp, ready for audit and post-incident review.
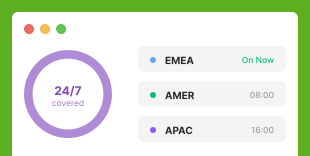
Timezone-aware rotations, follow-the-sun cover, and one-tap overrides keep a named responder accountable for every security incident, on every shift.
ITOC360 does not replace your SIEM or EDR. It makes sure their high-severity findings reach a person. When your detection stack confirms one of these, ITOC360 pages the on-call analyst and escalates until someone owns it.
ITOC360 receives alerts from your SIEM, EDR, cloud security, and SOAR tools out of the box, with no custom glue code required. 50+ native integrations and growing.
View All IntegrationsYes. Filter by severity or SIEM label so low-priority signals and brute-force noise stay in your SOC queue, while confirmed critical attacks page the on-call analyst by voice, SMS, or push.
Yes. ITOC360 ingests alerts from tools like Microsoft Sentinel, Elastic, CrowdStrike, AWS GuardDuty, and Google Security Command Center, and from automation platforms like n8n and Zapier, through native webhooks. Your detection and automation logic stays where it is.
Yes. Every alert, acknowledgment, and escalation step is captured with a secure, tamper-proof timestamp, and access is controlled with SAML SSO and role-based permissions, giving you a complete record for audit and compliance review.
Free to start, no card, and no agent to deploy in your SOC.